
iRhythm discloses data theft from third-party applications in cyberattack
iRhythm disclosed in a securities filing that it discovered a cyberattack on June 8 and the next day received a ransom message from a threat actor claiming to have stolen sensitive data, including proprietary data, patient protected health information, and other personal information. The company confirmed that some data was exfiltrated from third-party hosted business applications but stated that the incident did not affect clinical or medical device systems, nor did it impact manufacturing and distribution capabilities.
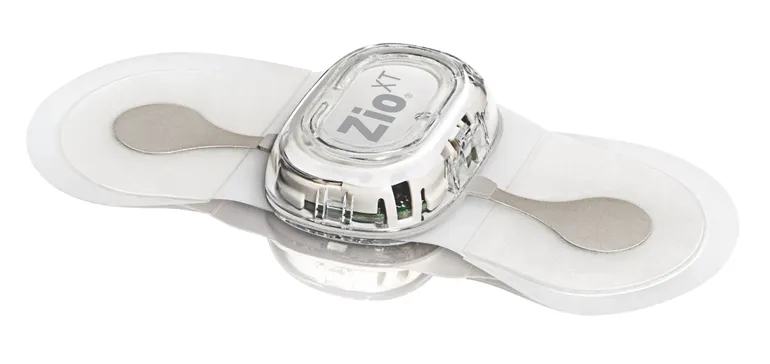
Heart monitoring device manufacturer iRhythm disclosed on Monday (June 12) that data from certain third-party hosted business applications was stolen in a cyberattack. In a filing with the U.S. Securities and Exchange Commission (SEC), the company said the attack was discovered on June 8, and it immediately activated its cybersecurity response plan.
According to the securities filing, the next day (June 9), iRhythm received a message from the threat actor claiming to have stolen sensitive information, including "proprietary data, patient protected health information, and other personal information." The threat actor demanded a ransom in exchange for not publicly disclosing the information. After receiving this communication, iRhythm confirmed that "certain data had been exfiltrated from these applications."
As of the time of this publication, iRhythm had not responded to MedTech Dive's request for comment on whether it has paid or plans to pay the ransom to the threat actor.
According to the securities filing, the data was obtained through social engineering tactics from certain third-party hosted business applications. The attack did not involve the company's clinical or medical device systems. As of Monday, iRhythm had found no evidence of ongoing unauthorized access to its systems, and the attack did not impact its ability to manufacture or distribute products.
"We have not identified any issues affecting our products, clinical or medical device systems, customer connectivity, manufacturing and distribution operations, patient safety, or our ability to meet patient needs," iRhythm said in a statement on its website. "Additionally, we do not store or retain personal financial account information or payment card information."
The company believes that, as of Monday, the incident is unlikely to have a material impact on its financial condition or results of operations. iRhythm has cybersecurity insurance that may cover some of the losses.
In addition to activating its cybersecurity response plan, iRhythm has engaged cybersecurity experts and external advisors to assist with the investigation.
"iRhythm is continuing to investigate the nature and scope of the incident, including the categories and volume of data involved and the affected individuals," the company said in the securities filing.
iRhythm is the latest medical technology company to suffer a cyberattack this year. In March, Stryker was hit by an attack that disrupted its ordering, shipping, and manufacturing for weeks and affected first-quarter results. In the same week Stryker disclosed the attack, surgical robotics company Intuitive reported a phishing incident in which an unauthorized third party accessed information including customer business and contact information, as well as employee and company data.
Meanwhile, Medtronic reported in April that an unauthorized party had accessed data in some of its corporate IT systems.